You can't leak data that isn't there
 Data & More
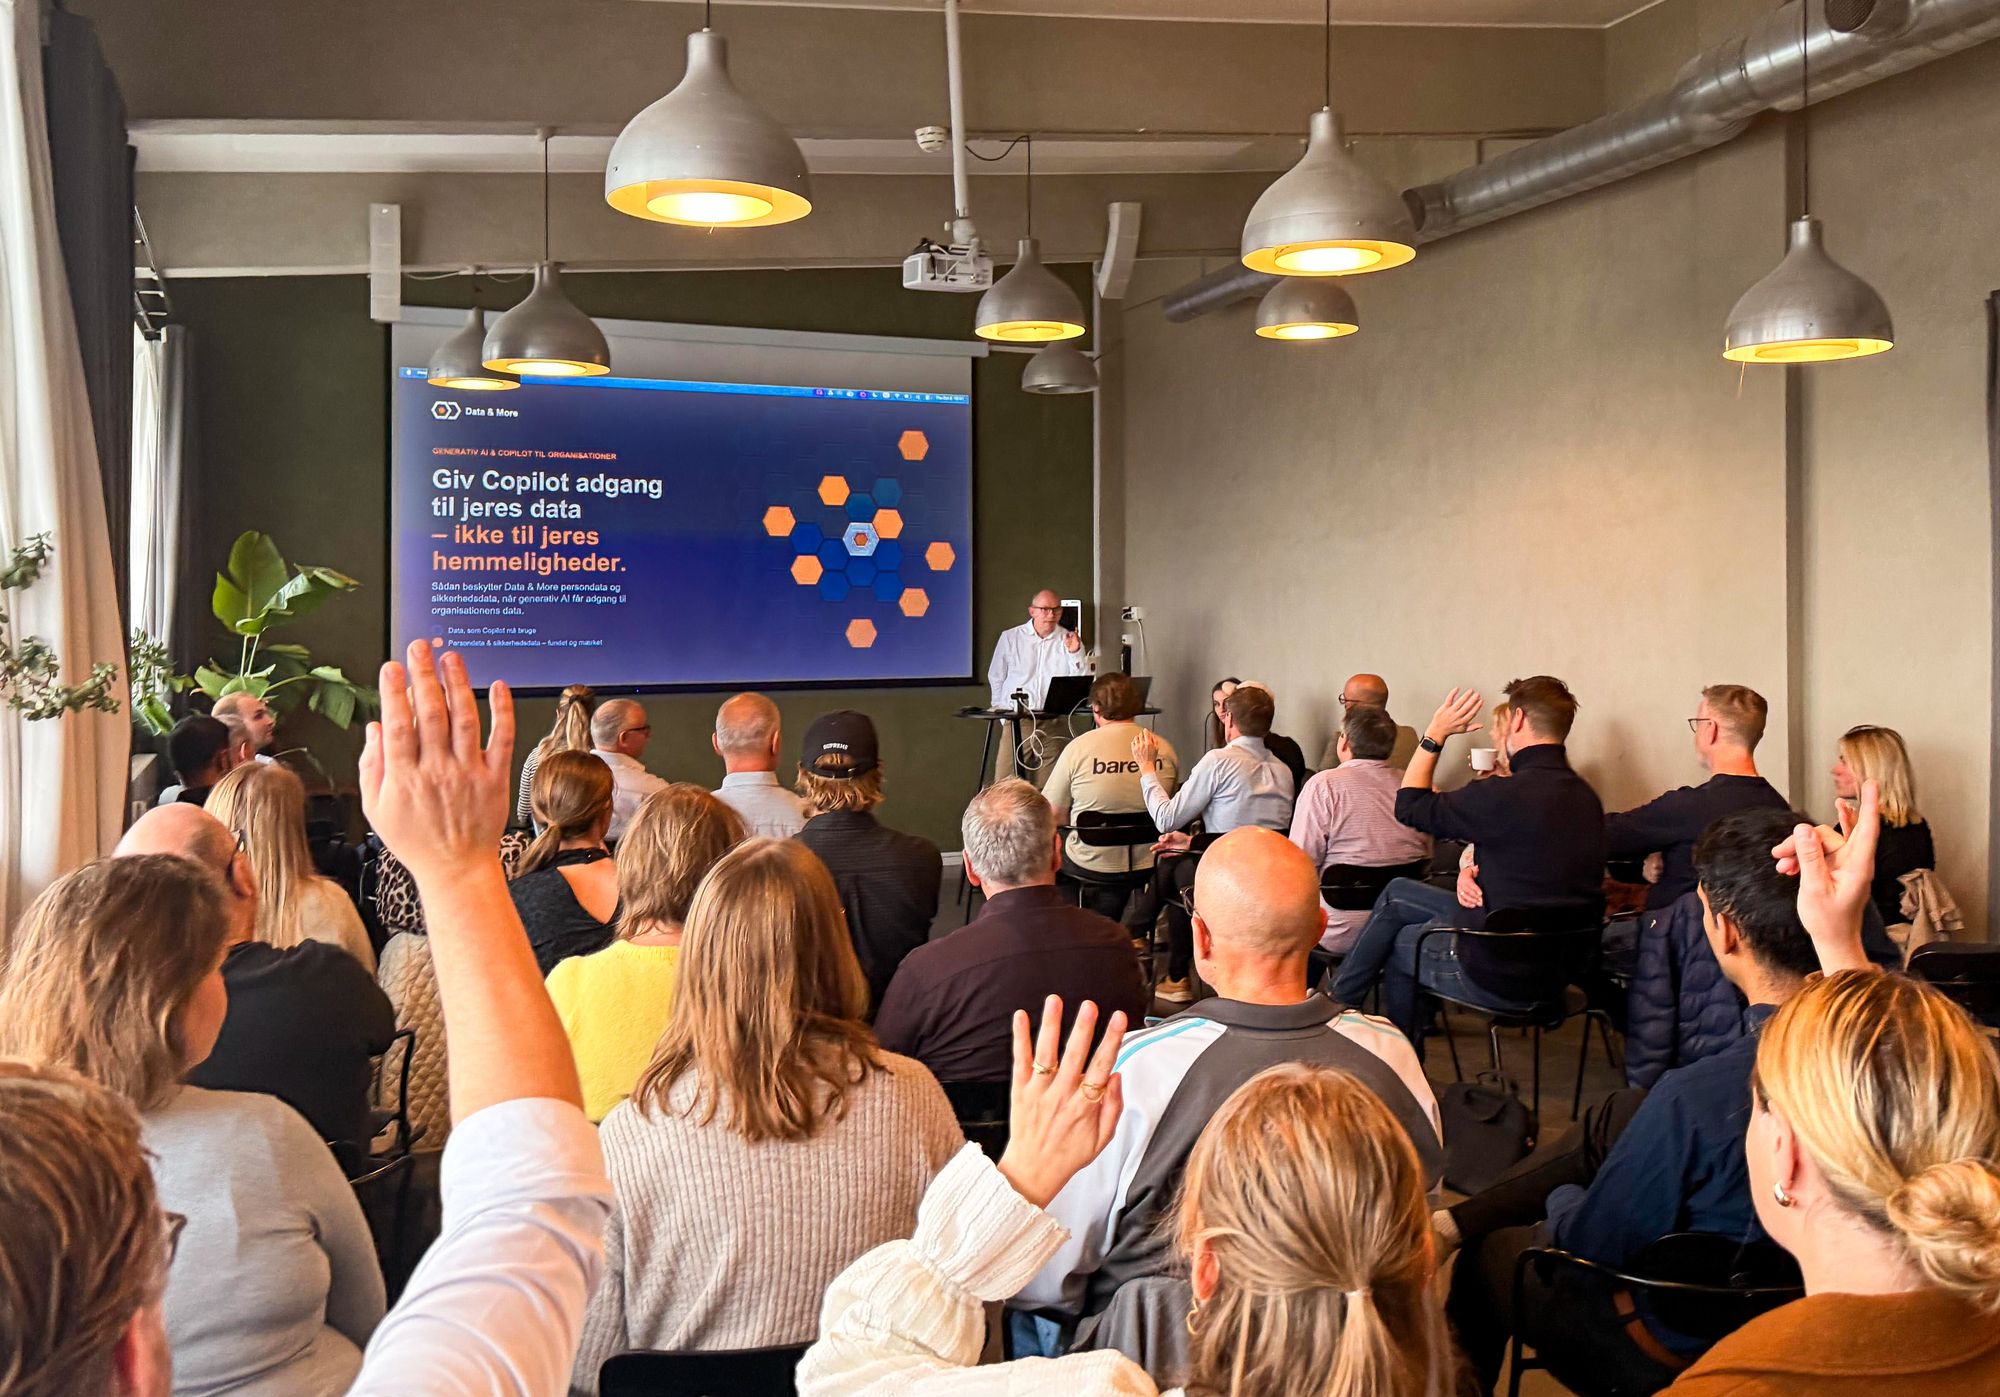
Copilot does not need to break in. It reads what your users can already reach. On 8 October we spent a morning at SOHO in Copenhagen on what that means for personal data and security data.
The seminar ran under the title "Få styr på persondata, før du giver AI adgang" [Get control of personal data before you give AI access]. Our thread for the morning was simple: you can't leak data that isn't there.
The full recording is below. Here are the highlights from each session.
Watch the full seminar:
View the slides here:
Finding the needle in the haystack
Sophia von Ferber and Mikkel Eidset Nielsson, who lead our German and Danish data classification, opened with the numbers behind the problem.
The average employee holds around 40,000 datasets, and only about 0.5% of them contain personal data. That makes classification a rare-event problem. To find 100 real hits you must classify 20,000 documents, and to keep 95% of flagged results correct you can afford just 5 false positives.
In other words, every single classification has to be right 99.975% of the time. Anything less and the people reviewing the results drown in noise.
Context decides, not the number
To make it concrete, the speakers introduced Bente, who has worked in HR for 20 years. When she cleans up her data, she should only see what needs a decision. And what she misses, Copilot can still find.
CPR numbers. A ten-digit number could be a CPR number [Danish personal identification number] or just an invoice number. Start words such as "CPR" or "cpr.nr" point to a CPR number, while stop words such as "Fakturanummer" [invoice number] rule it out. That is how an invoice overview is left alone, while an employee list on an HR SharePoint site is flagged and protected from AI.
Health data. Our grammar-based analysis reads a sentence like "Jeg har fået slidgigt" [I have got osteoarthritis] and only flags it when a person, an action and a health term are all present. It works in Danish, English and German. Context still matters: the same quote in a nursing thesis is not personal data, but in a named patient's medical record it is.
Feedback from more than 175,000 users keeps sharpening these rules. When a customer reports a miss, we build one global fix and roll it out to every customer.
Security data is the new attack surface
Until now, security meant protecting the network. With AI, the data itself is the attack surface: agents act across systems, inherit human access rights and work at machine speed. Data is no longer at risk because attackers go looking for it, but because it sits where an AI can reach it at any time.
The real (redacted) examples on screen made the point. Passwords sent in plain text by email, private keys zipped and mailed, penetration test reports listing every gap in a network, and firewall configurations saved to OneDrive. Once they are in Copilot's index, users cannot delete them.
Across roughly 160 scans we found 1,644,149 instances of critical security information, led by source code, passwords and log files. On average, 85% of mailboxes contain non-compliant data, and each employee has 16 emails with security information in plain text.
DLP on the platform you already use
Kristian Boe Helweg Hansen, our Customer Success & Compliance Manager and a certified DPO, showed how DLP builds directly on that classification.
ISO 27001:2022 control 8.12 describes how to prevent data leakage, while GDPR and NIS2 explain why. The DLP log is your evidence for all three.
One policy covers Exchange, OneDrive, SharePoint, Teams and Copilot. In the demo, CPR numbers, passports, customer data and health data were blocked, while salary data and payment card numbers triggered an alert. It runs in the same Data & More platform used for clean-up, with no new console or agent. We recommend starting in Alert mode, and the setup is built to fail safe, so mail keeps flowing if DLP ever stops.
Every event lands in one audit trail: channel, user, data class, action and who released it, ready to export for your auditor.
Keeping secrets out of Copilot
Kristian Billeskov Bøving, PhD, our Head of AI and a former Director at Gartner, closed the programme. His starting point: Copilot only creates real value with access to your data, and that same access creates the risk.
He presented the three tools that let Copilot work with your data without reaching what it shouldn't:
Copilot Protection labels personal and security data so Copilot leaves it alone.
Copilot Deletion brings Copilot chats and uploaded files into your reports and deletion procedures.
Copilot DLP warns users when Copilot is used the wrong way.
Where to start
Each layer builds on the one before. Classification finds the data, deletion removes what has no purpose, and DLP and Copilot controls protect what remains. Organisations already classifying with Data & More have the first layer in place, so DLP and the Copilot tools run on results they already trust.
For everyone else, the starting point is the same as the seminar's: knowing what actually sits in your mailboxes, OneDrives and SharePoint sites. A free review shows exactly that.
Thank you to everyone who joined us at SOHO.
Data & More
Because you can't leak data that isn't there